On Tuesday, September 29, 2020 AS1221 - Telstra announced 472 prefixes in a BGP hijack event that affected 266 other ASNs in 50 countries, with the most damage rendered to the U.S. and UK based networks. Worldwide it affected more than 1680 IPv4 prefixes, creating almost 2000 path challenge conflicts.
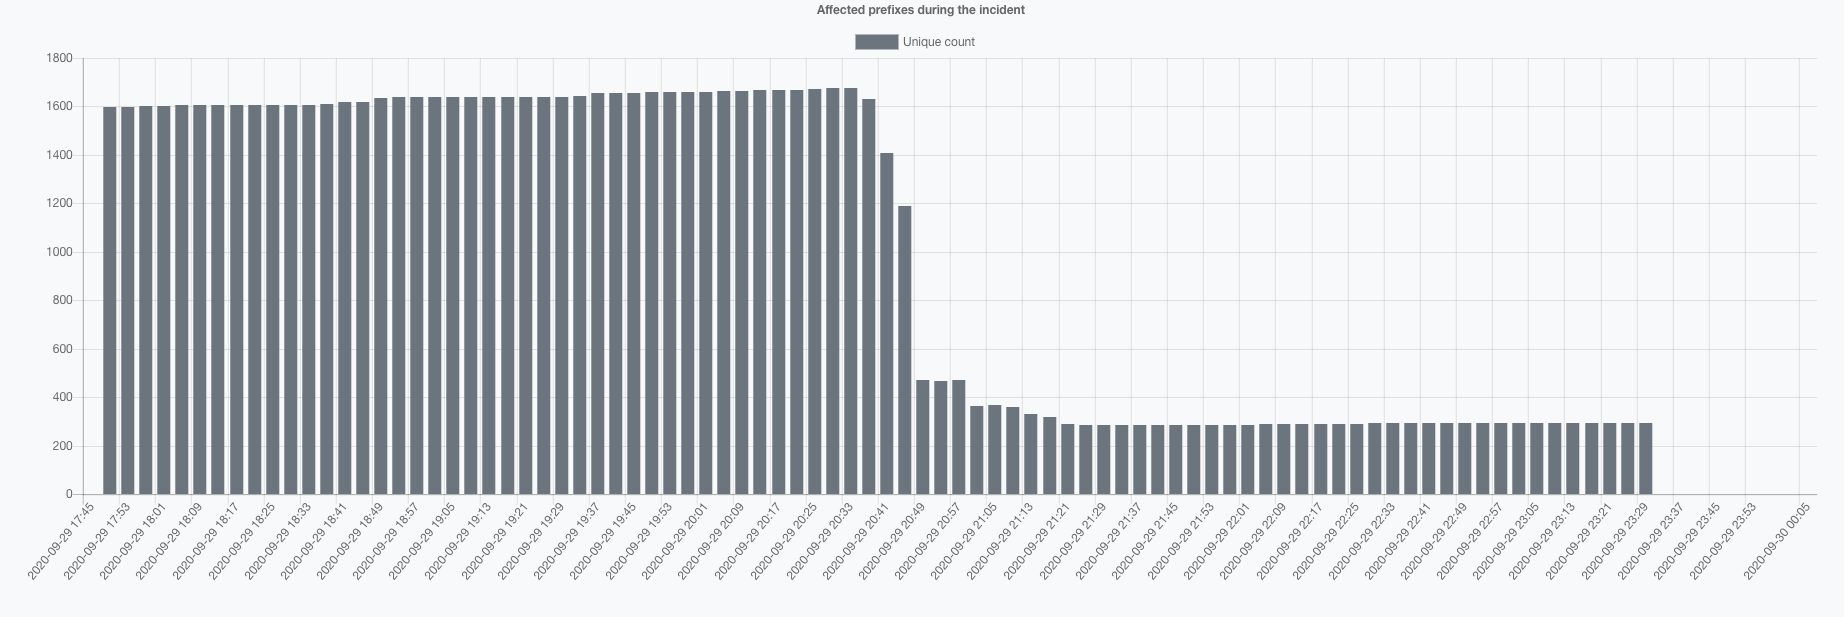
This incident peaked in affected prefixes for three hours straight, starting at 17.50 UTC and dropping under 400 affected prefixes only after 21.00 UTC. ROAs were in place for some of the hijacked prefixes, approximately between 20-25%.
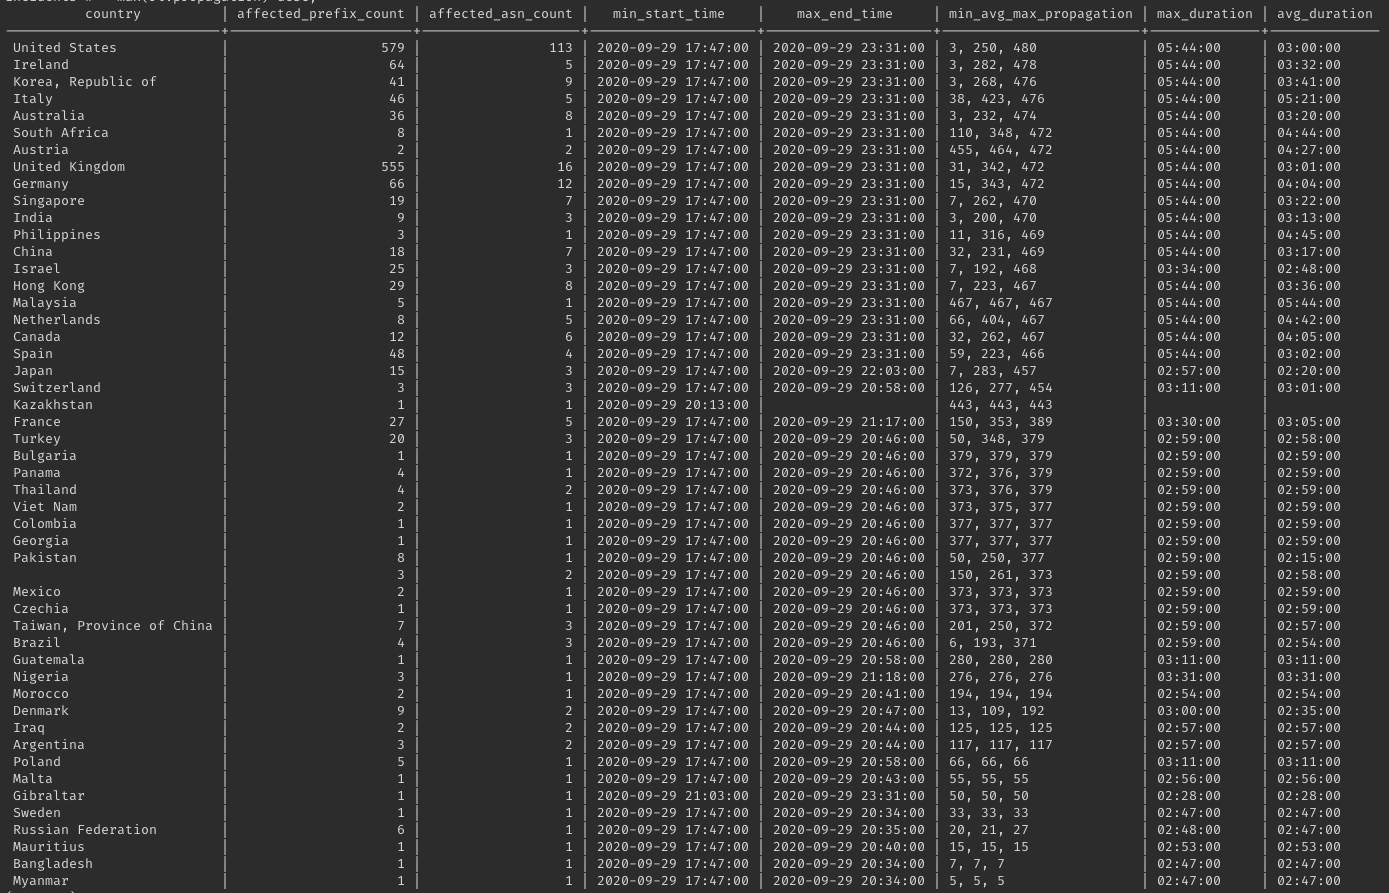
ProtonMail was one of the first to report the ongoing BGP hijack via their Twitter account, and after four hours Telstra commented on the thread:
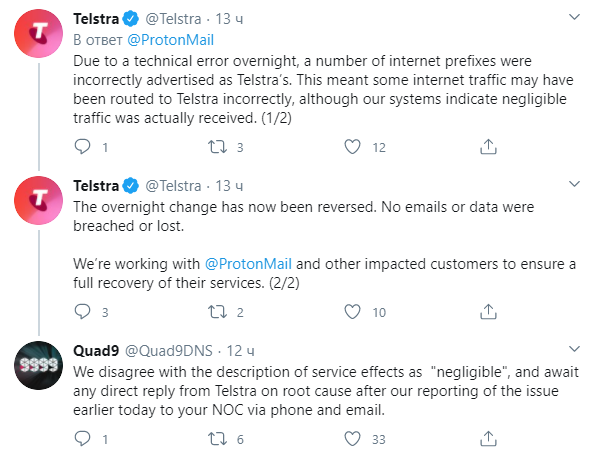
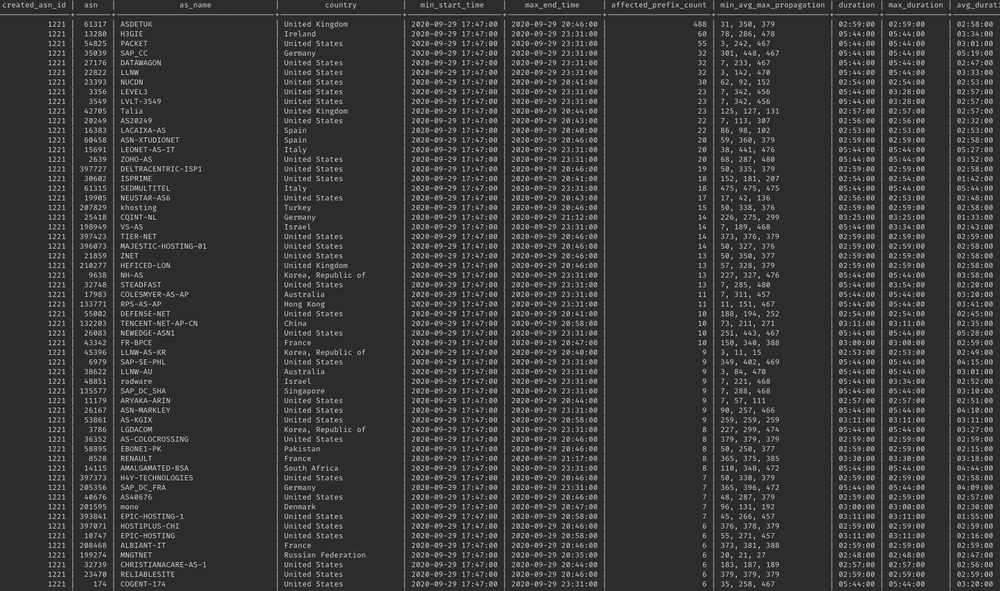
A careful reader can spot a wide range of high profile names among affected ASes as the hijack spread mostly through AS4637 - Telstra’s another autonomous system with an “unspecified” relation to the AS1221.
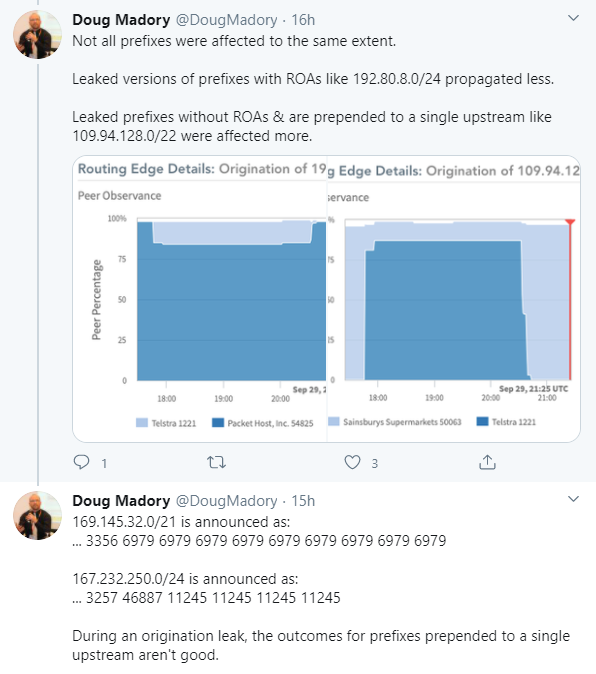
Doug Madory from the Oracle Internet Intelligence team reported incident details as it was happening:
As a conclusion, we want to remind you to sign your routes. Right now, this is the only viable strategy to minimize the damage of a potential BGP hijack.


Share your experience and expectations regarding DDoS protection. Your answers will help us tailor solutions to meet your cybersecurity needs.
Tell us about your company’s infrastructure and critical systems. This will help us understand the scope of protection you require.
Help us learn about how decisions are made in your company. This information will guide us in offering the most relevant solutions.
Let us know what drives your choices when it comes to DDoS protection. Your input will help us focus on what matters most to you.


