Qrator Availability Network allows small and large businesses to protect their applications from all types of DDoS attacks, regardless of bandwidth or complexity.
Qrator Labs own unique geo-distributed filtering network based on united BGP Anycast architecture provides reliable, low latency web infrastructure protection from any network attacks leading to unavailability of web resources.
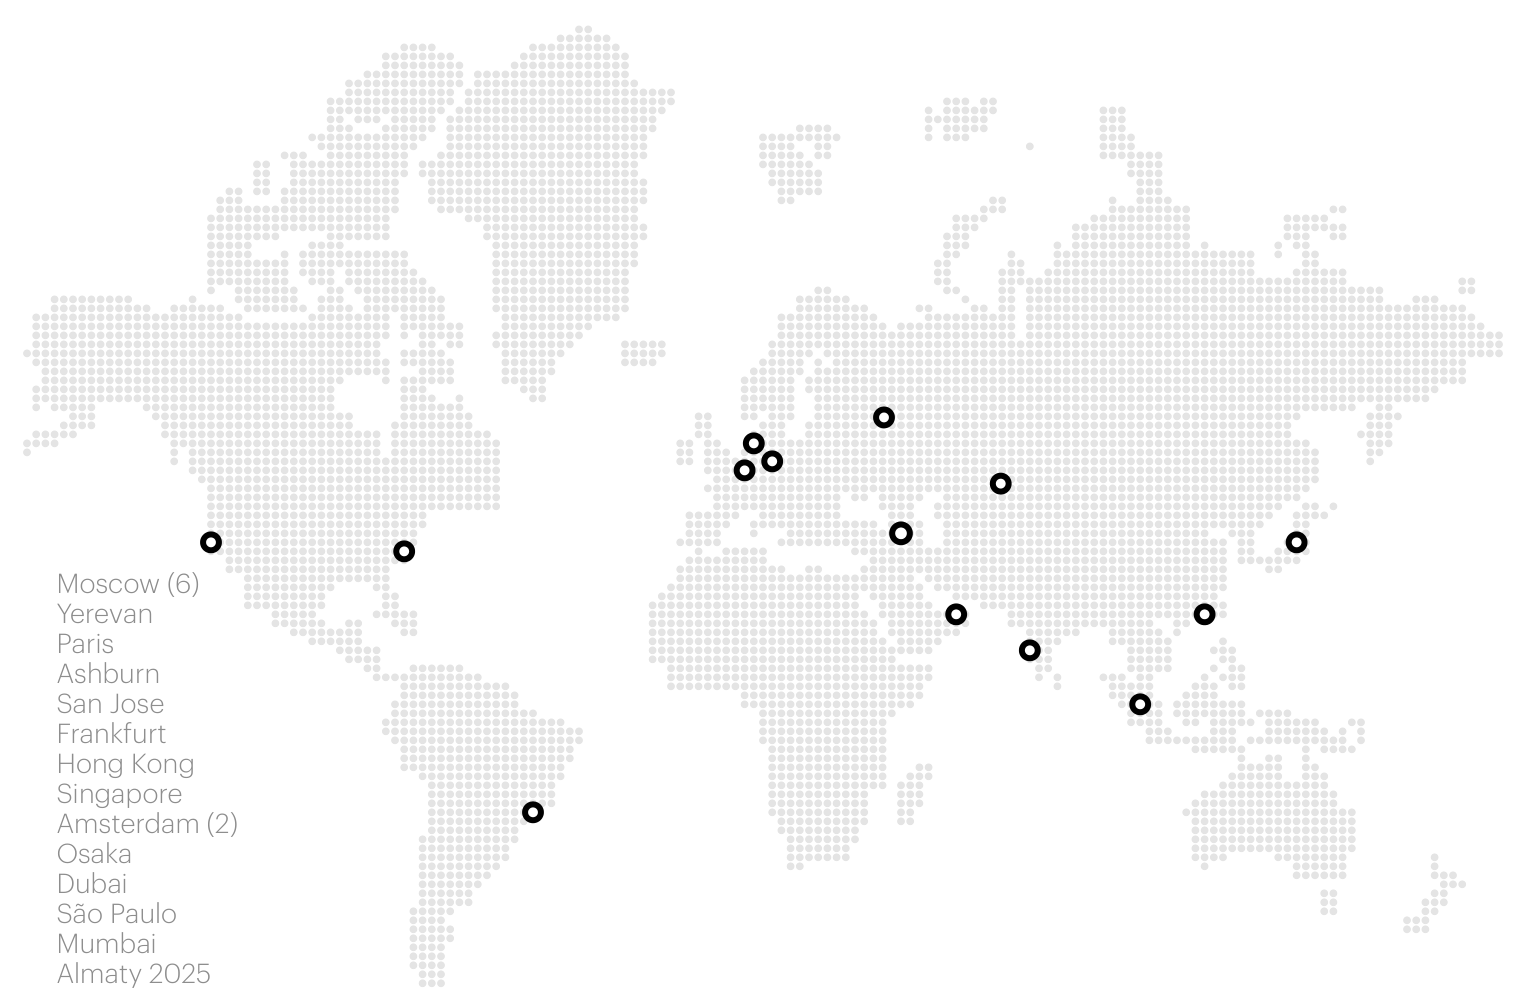
With 15 scrubbing centers around the globe and throughput of more than 4,000 Gbps Qrator Labs filtering network ensures excellent connectivity in the regions of North America, LatAm, Europe, MENA, and APAC. Qrator Labs filtering centers are located in global points of the Internet traffic concentration, connected to transcontinental TIER1 providers as well as leading regional backbone Internet providers.
The Qrator Labs network automatically provides security up to and including the L7 (application layer) on all billing plans and for all customers.
Customers don't pay for the service in case it does not meet the declared quality (guaranteed by a contract).
BGP-Anycast guarantees a geographically distributed, fault-tolerant network to protect applications with a high degree of connectivity. Failure of any filtering node will have no impact on the quality of service and performance of customers' applications due to traffic balancing between major Internet service providers.
Any web infrastructure may be protected within 15 minutes with two connection methods: DNS and BGP.
No need for manual configuration or involvement of qualified specialists to get reliable protection against complex DDoS attacks.
The Qrator Labs API can be integrated with your authentication system, database or device monitoring service providing a wide range of system managing features.
We don't use CAPTCHA or other annoying user checks.
Online Ticket System Dashboard, phone, email, and chat support. Response time is less than 15 minutes to every customer's request.
HTTPS filtration with no key disclosure allows to analyze and filter HTTPS traffic without disclosing encryption keys and without breaching the customer’s security policies.
Can improve a website's SEO by reducing page load times and improving security.
Traffic is analyzed at all layers of the protocol stack, including the application layer (the seventh layer of the OSI model). The traffic of application-level attacks closely resembles the activity of ordinary users, which makes them very hard to detect and neutralize.
By continuously studying the traffic patterns regardless of the DDoS attacks, Qrator Labs improves the algorithms and makes online adjustments to the available filtering methods, allowing it to detect any anomalies and respond immediately to DDoS attacks.
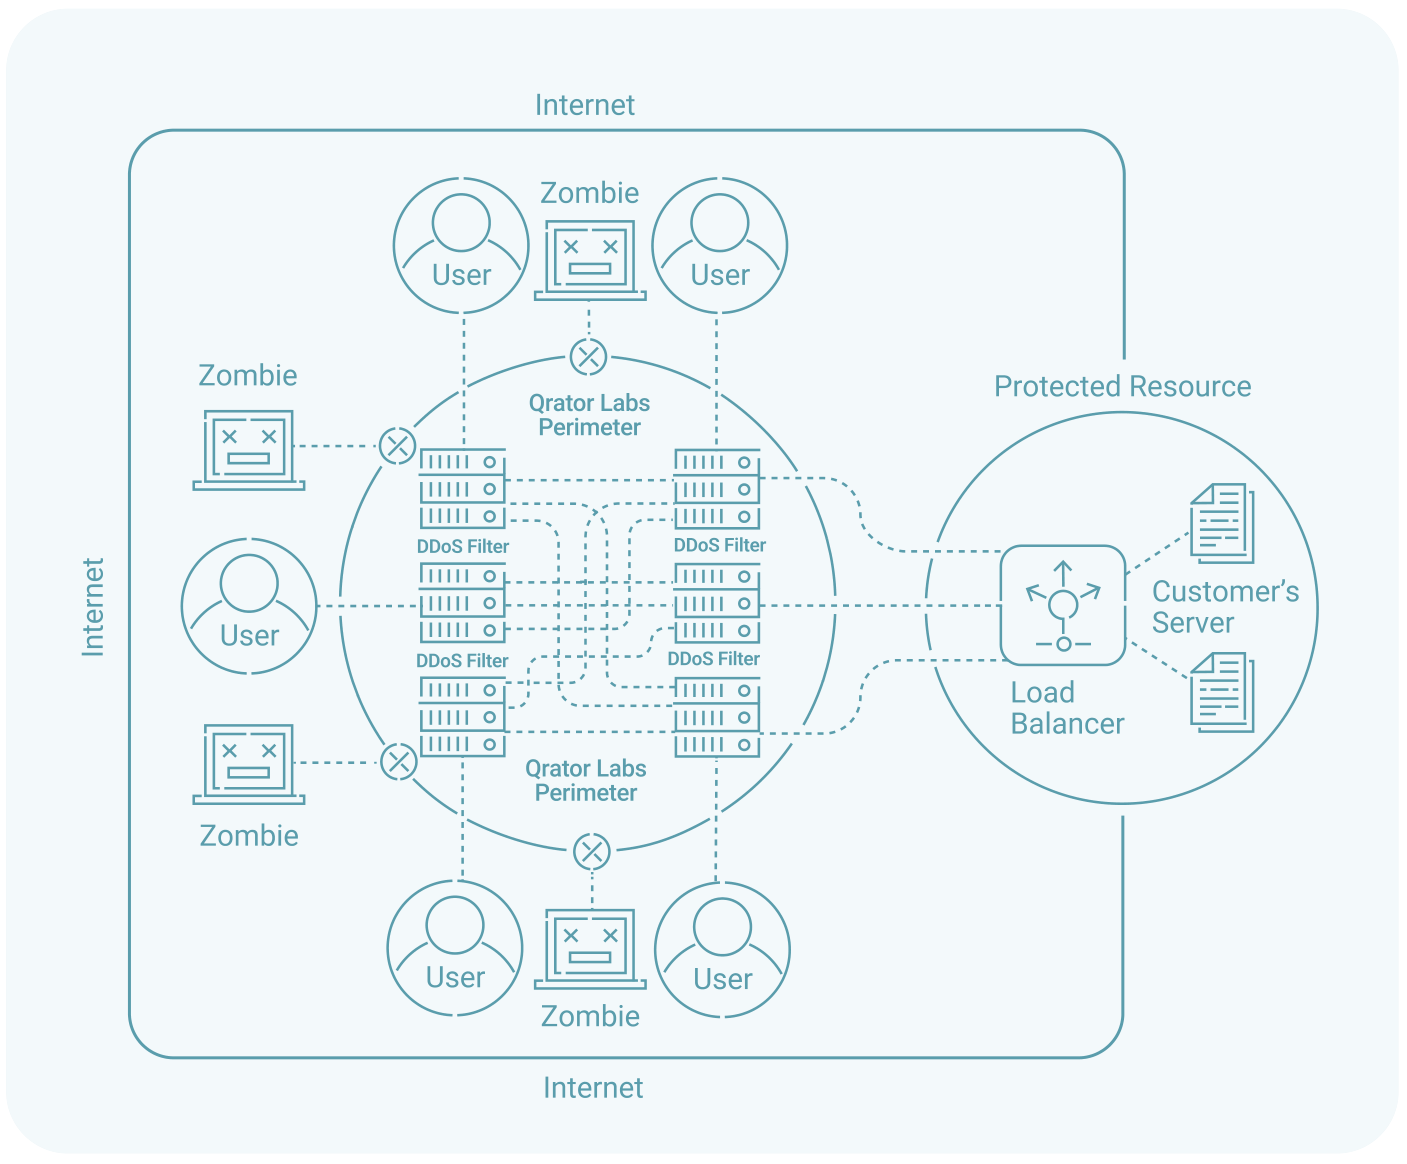
The filtered traffic is forwarded to the protected site either through the public Internet or through a specially deployed L2 VPN. DDoS attack traffic is blocked at the perimeter of the Qrator Labs network, never reaching the client's resources. Qrator Labs network operation is completely invisible, both to the business and its website visitors, and Qrator Labs clients will eventually learn about the attack only from the reports in their personal accounts.
You get a 7-day trial period in case your application is not under a DDoS attack, or a 1-day trial period if you come under attack.
You can access the results of the analysis of your application's traffic for any period you've been using our services. Using the API, you can connect your existing monitoring system (Nagios, Zabbix etc.) with Qrator Labs and receive notifications on the incidents in the format most convenient for you.
Using the API, you can connect your existing SOC / monitoring system / SIEM with Qrator Labs and receive notifications on the incidents in the format most convenient for you.
The algorithms implemented by Qrator Labs allow the determination of the cause for increasing resource attendance — whether it is a DDoS attack or rising interest from the visitors.
Qrator Labs reaction time to a DDoS-attack — up to 30 seconds in 97% of attacks vectors