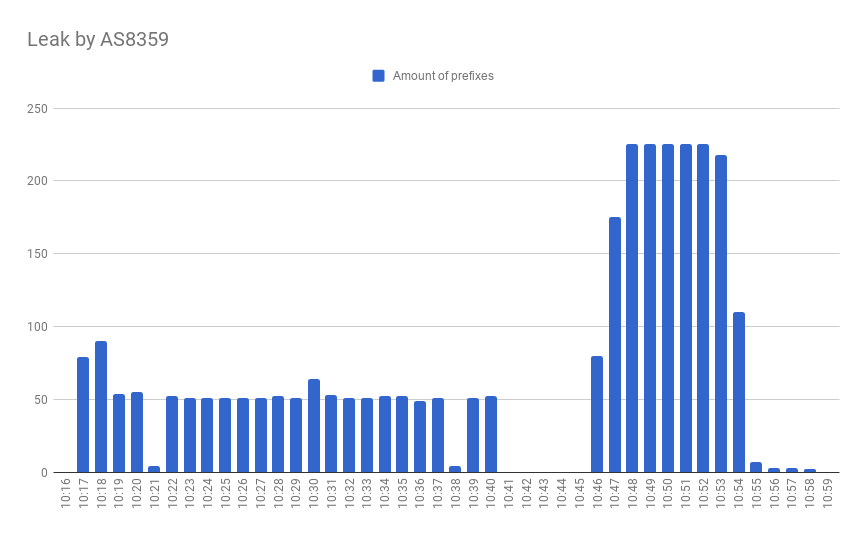
February 7, 2020 - one of the biggest carriers and ISPs in Russia - MTS - AS8359, created two route leaks involving prefixes belonging to such companies as Imperva, GCore, IPTP, Akamai and many others. MTS took those prefixes from HKIX (AS4635) and sent them to Level3 (AS3356) for further distribution.
According to Radar.Qrator’s statistics gathered on the incident, 36 ASNs were involved, with 225 prefixes at peak containing more than half a million individual IP-addresses. Most of them belonged to AS35916 whose /16 network was affected by the route leak.
Our blind guess on the cause of this incident is that something was not working correctly at MTS (or one of its subsidiaries, like broadband ISP MGTS) and they accidentally created a leak while trying to troubleshoot.


Share your experience and expectations regarding DDoS protection. Your answers will help us tailor solutions to meet your cybersecurity needs.
Tell us about your company’s infrastructure and critical systems. This will help us understand the scope of protection you require.
Help us learn about how decisions are made in your company. This information will guide us in offering the most relevant solutions.
Let us know what drives your choices when it comes to DDoS protection. Your input will help us focus on what matters most to you.


